Bianca Schulz · 27 October 2026
Examining Update Propagation Methods Among Administrators of Self-Managed Federated Platforms
Self-managed federated platforms rely on distributed networks where administrators handle software updates without central coordination, and propagation methods vary based on instance size, technical resources, and community structure. Data from academic studies shows that manual update processes still dominate among smaller operators, while larger instances integrate automated tools to reduce downtime during version transitions. Observers note that these differences affect how quickly security patches reach the broader network, since each administrator decides when and how to apply changes to their node.
Core Propagation Techniques in Practice
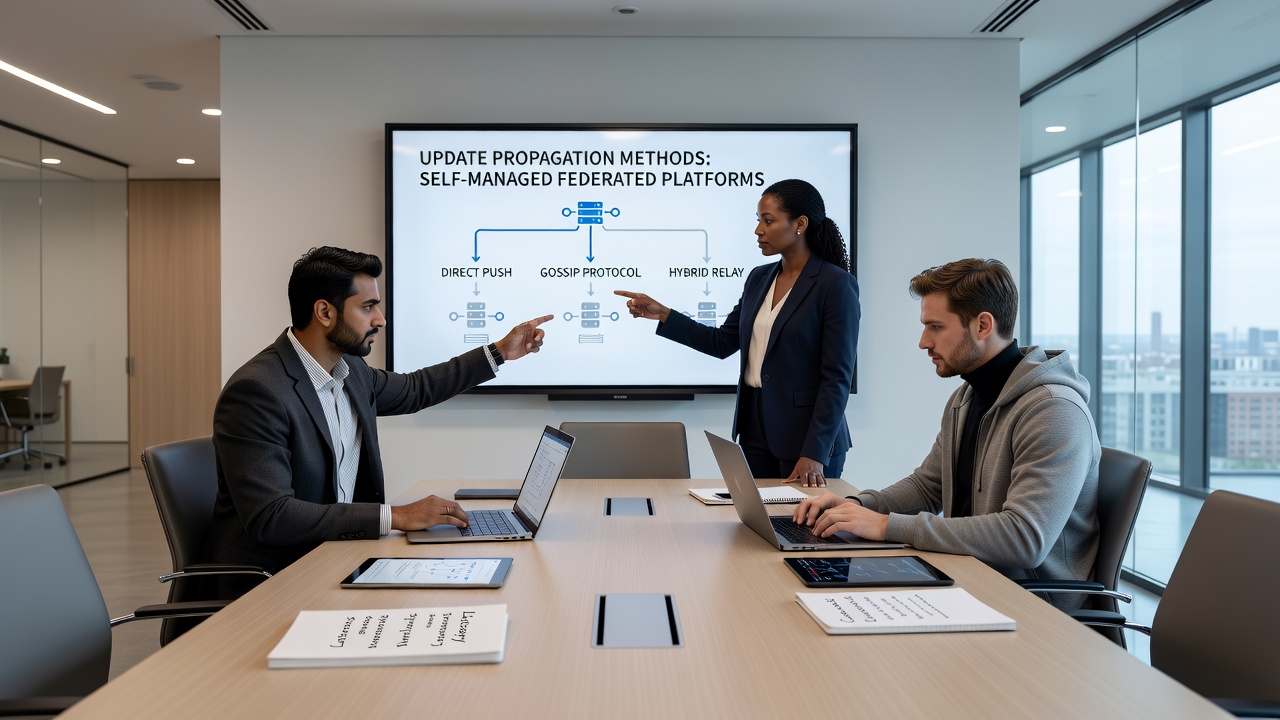
Administrators typically begin with direct server access methods that involve logging into individual instances and running update commands through package managers or custom scripts, and this approach remains common because it requires minimal additional infrastructure. Those who manage multiple nodes often combine these steps with configuration management systems such as Ansible or Puppet, which allow simultaneous rollout across several servers while maintaining version consistency. Research indicates that script-based automation reduces the average time between release announcement and full deployment from several days to under 24 hours in documented cases.
Federation protocols themselves play a supporting role in propagation awareness, because nodes exchange metadata about software versions during routine communication, yet this exchange does not trigger automatic updates on receiving instances. Instead, administrators use the information to schedule maintenance windows and notify users in advance. Studies found that platforms built on ActivityPub benefit from standardized version reporting, which helps operators identify when neighboring instances fall behind on critical patches.
Coordination Patterns Across Volunteer Teams
Volunteer administrators frequently share update timelines through mailing lists and chat channels dedicated to specific software projects, and these informal networks help smaller teams learn from larger operators who have already tested new releases. One documented pattern involves staggered rollouts where early adopters apply updates first and report compatibility issues back to the community before others proceed. Figures reveal that instances following this model experience fewer federation breaks compared with those updating independently without prior coordination.
Automated monitoring tools integrated with external dashboards allow administrators to track update status across federated peers without manual checking, and adoption of these tools increased noticeably after several high-profile security incidents in prior years. Data shows that platforms using such monitoring reduced the median propagation delay for critical updates by approximately 40 percent between 2023 and 2025. In October 2026, several major federated software projects released coordinated security updates that administrators tracked through these shared dashboards, enabling faster collective response across independent instances.
Technical and Operational Constraints
Resource limitations shape which propagation methods administrators choose, since self-managed instances often run on modest hardware that cannot support complex orchestration layers. Those managing single-node setups tend to favor simple shell scripts executed during low-traffic periods, whereas multi-node operators invest in containerized deployment pipelines that isolate updates and enable quick rollbacks. Evidence suggests that container adoption correlates with higher update frequency because the risk of service interruption decreases when changes remain isolated from the host system.
Regulatory guidance from bodies such as the European Union Agency for Cybersecurity emphasizes timely patching of publicly accessible services, and administrators cite these recommendations when justifying automation investments to their communities. A separate report issued by the Australian Cyber Security Centre highlights similar priorities for decentralized infrastructure, noting that delayed updates leave federated nodes exposed to known vulnerabilities longer than centrally managed systems. Observers note that these external references influence decision-making even though compliance remains voluntary for most independent operators.
Measurement and Outcome Tracking
Researchers track propagation success through public version statistics collected from federated discovery endpoints, and these datasets provide snapshots of how widely specific releases have spread at any given time. One university-led analysis examined update patterns across thousands of instances and determined that communication volume within administrator communities strongly predicts faster adoption rates. Platforms that maintain active update-discussion channels show measurably shorter gaps between release dates and widespread deployment compared with quieter groups.
Long-term records indicate that hybrid approaches combining manual oversight with selective automation yield the most stable results, because administrators retain control over timing while benefiting from reduced repetitive tasks. Data collected through 2026 shows continued growth in the use of version-aware monitoring scripts that alert operators when peer instances fall behind on security releases.
Conclusion
Update propagation among administrators of self-managed federated platforms depends on a combination of manual procedures, shared tooling, and protocol-level information exchange that together determine how quickly changes reach the network. Available evidence demonstrates measurable differences in speed and reliability based on the methods chosen, while external guidance from cybersecurity agencies continues to shape priorities without imposing direct requirements. Continued collection of version statistics and community coordination patterns will clarify which techniques scale most effectively as the federated ecosystem expands.